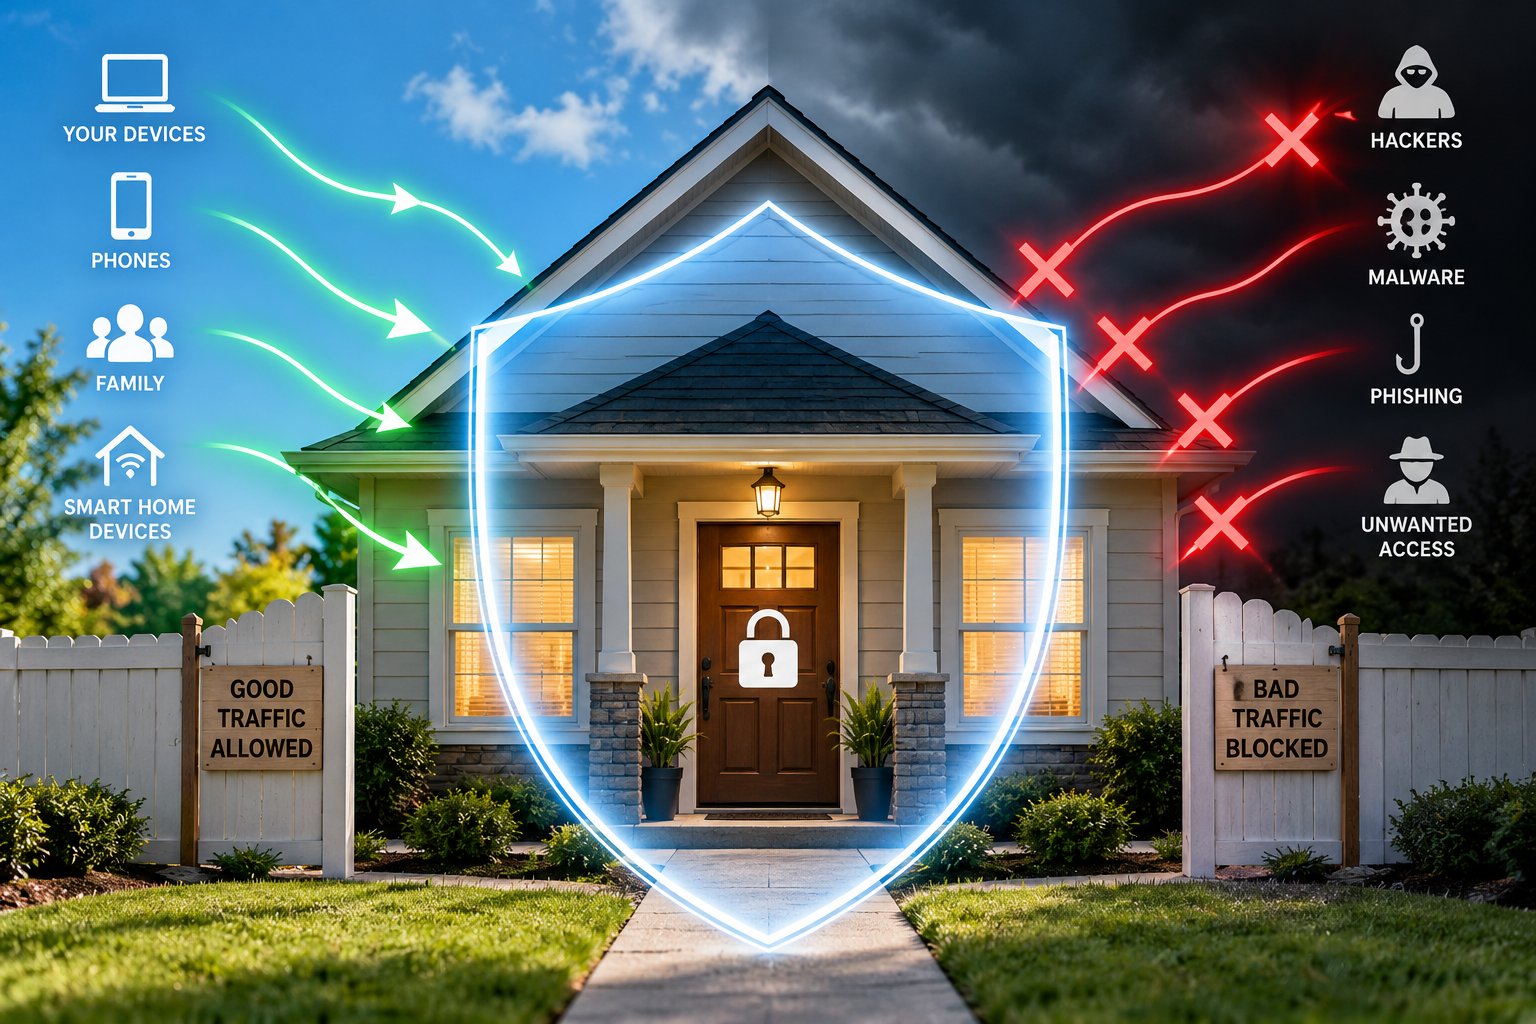
Criminal defense cases involve privileged communications that prosecutors would love to access. Your clients' communications with you are legally protected - but only if you keep them confidential.
The Stakes: Privilege Is Only As Strong As Your Technology
Criminal defense is one of the highest-stakes practice areas. Your clients are sharing details with you that they might not share with anyone else - sometimes their freedom depends on attorney-client privilege. And that's exactly why your systems are a target.
Here's what we've learned: privilege is only as strong as your technology. Courts have ruled that transmitting privileged communications over unsecured channels can constitute a waiver of privilege. Translation: if your email isn't encrypted, if your files are stored insecurely, or if an attacker gains access to your communications, a prosecutor might be able to use that information against your client.
Beyond the legal risk, there's the practical one. Criminal cases involve sensitive investigation details, witness information, and case strategy. If that information falls into the wrong hands - whether it's an attacker, a corrupt law enforcement officer, an overly aggressive private detective, or the prosecution - your case could be compromised before trial even begins.
Your Professional Obligation: ABA Rules 1.1 and 1.6
You're not just dealing with a technical issue - you're facing a professional responsibility issue. The American Bar Association has made your cybersecurity obligations crystal clear:
- ABA Model Rule 1.1 (Competence): Attorneys are now expected to maintain a working knowledge of the benefits and risks of technology relevant to their practice. This includes understanding how your systems protect - or fail to protect - client information. The ABA's formal guidance makes clear that failing to protect client data, including digital records and communications, can constitute a breach of your duty of competence. If you're running a criminal defense practice with unsecured email or unencrypted files, you're not meeting this standard.
- ABA Model Rule 1.6 (Confidentiality of Information): You are required to make reasonable efforts to prevent the unauthorized disclosure of client information. The rule doesn't just apply to physical files in your office - it explicitly covers your technology systems. 'Reasonable efforts' now includes encryption, access controls, secure backups, and regular security assessments. A prosecutor obtaining client communications through a security breach isn't just a personal injury case waiting to happen; it's evidence that you didn't meet your ethical duty under Rule 1.6.
These aren't aspirational guidelines. They're your professional responsibility. And if there's a breach that could have been prevented by reasonable security measures, you're exposed to malpractice claims, ethics complaints, and potential suspension.
What Attackers Know (And What You Should Too)
Criminal prosecutors aren't the only threat. Your firm is a target for:
- Ransomware operators: They know defense firms hold high-value data. Locking up your case files and demanding payment before trial is a tactic we've seen escalate.
- Sophisticated phishing campaigns: Attackers posing as clients, opposing counsel, or court officials to trick staff into revealing credentials or downloading malware.
- Corrupt law enforcement or private investigators: Yes, this happens. Someone with a badge or a retainer from the prosecution might try social engineering to access your communications.
- Disgruntled employees or departing staff: Without proper access controls, anyone with a laptop could copy sensitive case files.
- Nation-state actors: In high-profile cases, adversarial countries have been known to target U.S. defense counsel to gather intelligence.
Here's What We Typically Recommend for Criminal Defense Practices
- End-to-end encrypted email: All electronic client communications must be encrypted so that even your email provider can't read them - and prosecutors can't intercept them.
- Secure cloud storage for case files: Files need strong access controls, encryption at rest and in transit, and detailed audit logs showing who accessed what and when.
- Multi-factor authentication on all systems: Every login - email, file storage, VPN, practice management software - requires a second factor. A password alone isn't enough.
- Regular staff training on phishing recognition: Criminal investigators sometimes pose as clients or authorities. Your team needs to spot these attempts and know the protocol for verifying identity.
- A clear protocol for verifying client identity: Before sharing sensitive case strategy or discovery, verify you're actually talking to your client. Secure communication channels help, but protocols matter too.
- Automated backups of all case files: Losing critical evidence or strategy documents to ransomware isn't just operationally devastating - it's a breach of your duty to your client. Backups must be tested and recoverable within hours, not days.
- Regular security audits: Catch vulnerabilities before an attacker does. An annual assessment plus targeted audits after any personnel changes or system upgrades is standard practice now.
What We've Seen When Defense Firms Get This Right
Many defense firms implementing these protections actually made them more effective operationally. Clients trust them more - because they know their communications are secure. Documentation is more organized when it's centralized and access-controlled. Staff is more confident because they're not worried about accidentally forwarding something to the wrong person or falling for a phishing attack. And there's no lingering doubt about whether privilege was properly maintained.
Even more importantly: when a security audit is needed, these firms can demonstrate due diligence. That's not just professional protection - it's peace of mind.
Your Move
In criminal defense, privilege is everything. Your clients' freedom can depend on it. But privilege isn't maintained by good intentions - it's maintained by security practices that are as serious as the cases you handle.
If you're unsure whether your current systems meet ABA Rules 1.1 and 1.6, that's exactly the kind of conversation you should be having. Let's talk about building a practice where confidentiality is genuinely guaranteed - not just in theory, but in practice.